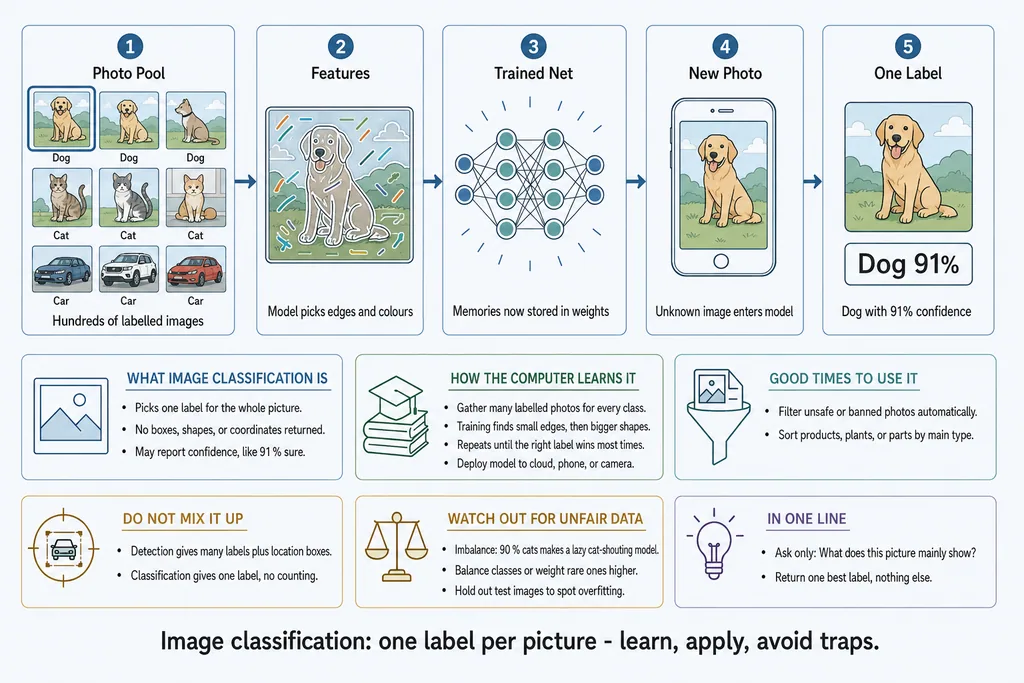
 You can see it again
Under pressure people bring back shapes and positions long after the wording has gone.
Picture superiority · Shepard 1967, Standing 1973 Examers.io
 F5
The F5 Certified Technology Specialist, BIG-IP APM certification validates your ability to implement, troubleshoot, and maintain BIG-IP Access Policy Manager (APM) across a variety of application environments. It focuses on authentication, authorization, and accounting (AAA) resources, SAML federation, access control lists, and single sign-on. Earning this credential demonstrates that you can secure and manage access to applications using F5's TMOS-based solutions.
Content last reviewed 30 July 2026 · Up to date
What this certification covers, who it is written for, and what the exam itself looks like on the day.
What it validates, who it is written for, and the experience it assumes.
The F5 Certified Technology Specialist, BIG-IP APM certification validates the skills and understanding required for day-to-day management of application delivery networks that incorporate technologies based on the TMOS operating system. It emphasizes the implementation, troubleshooting, and maintenance of BIG-IP APM in various application environments, with special focus on different types of authentication, authorization, and accounting resources.
Candidates who earn this certification demonstrate proficiency in configuring SAML federation, defining Layer 4 and Layer 7 access control lists, applying single sign-on profiles, and understanding all access policy modes. This credential is a prerequisite for the Security Solutions Expert certification track, making it a foundational step for professionals pursuing advanced security expertise.
This certification is for network and security professionals who manage application delivery networks and need to implement, troubleshoot, and maintain BIG-IP APM in a variety of application environments. It is ideal for those who work with authentication, authorization, and accounting resources, SAML federation, and access control. The minimally qualified candidate is proficient in various authentication mechanisms used to provide security and access management for different types of applications, and can configure, implement, troubleshoot, and maintain BIG-IP APM without assistance.
F5 recommends that candidates have a valid F5-CA, BIG-IP certification and hands-on experience with BIG-IP APM in production environments. Experience with BIG-IP LTM and APM modules; Understanding of authentication, authorization, and accounting (AAA) resources; Familiarity with SAML federation and single sign-on concepts; Knowledge of access control lists and portal objects
Every domain and objective F5 measures, with the weight they carry on the exam.
The official F5 exam outline · checked 30 July 2026 · See the source
Everything F5 publishes about sitting it, and nothing we inferred.
Valid F5-CA, BIG-IP certification
The path F5 lays out, how the credential is kept, and where to book.
Step-by-step path to F5 Certified Technology Specialist, BIG-IP APM
Credential earnedF5 Certified Technology Specialist, BIG-IP APM CertificationThis certification is currently active and available. F5 maintains this certification to validate current skills and industry relevance.
Register for the exam through Pearson VUE, F5’s authorized testing partner.
Schedule your examVisit the official F5 certification page for exam policies and requirements.
View the official pageYour coach in the app reads what you have answered with the book closed and tells you one thing to do tonight. It will not count an answer you gave with the page open, and it will tell you when you are not ready.
See how the coach worksYes. Receiving the BIG-IP APM Specialist certification is a prerequisite for the Security Solutions Expert certification track.
After the first failed attempt, you must wait 15 days. The second failure requires a 30-day wait, the third a 45-day wait, the fourth a one-year wait, and the fifth or more a 90-day wait. Your retake count resets only when you pass the exam.
Yes, but you must do so at least 48 hours before your scheduled exam time. Rescheduling within 48 hours incurs a fee. You must modify your appointment yourself; F5 Support, Pearson VUE, and Certiverse cannot process rescheduling or cancellation requests.
You must bring two forms of valid, signed ID. One must be government-issued and include a photo. The name on your ID must match the name on your F5 Certified account.
Yes. F5 offers a practice test developed from the same blueprint as the live exam. It costs US $20 and can be viewed through the F5 Education Services Portal.
This certification is designed for professionals who manage application delivery networks and are responsible for implementing, troubleshooting, and maintaining BIG-IP APM, including security and access management for applications.
The official exam page does not specify a hands-on lab component. The exam is proctored and delivered at Pearson VUE testing centers.
Every domain, every objective, and every concept F5 measures — each one written out.
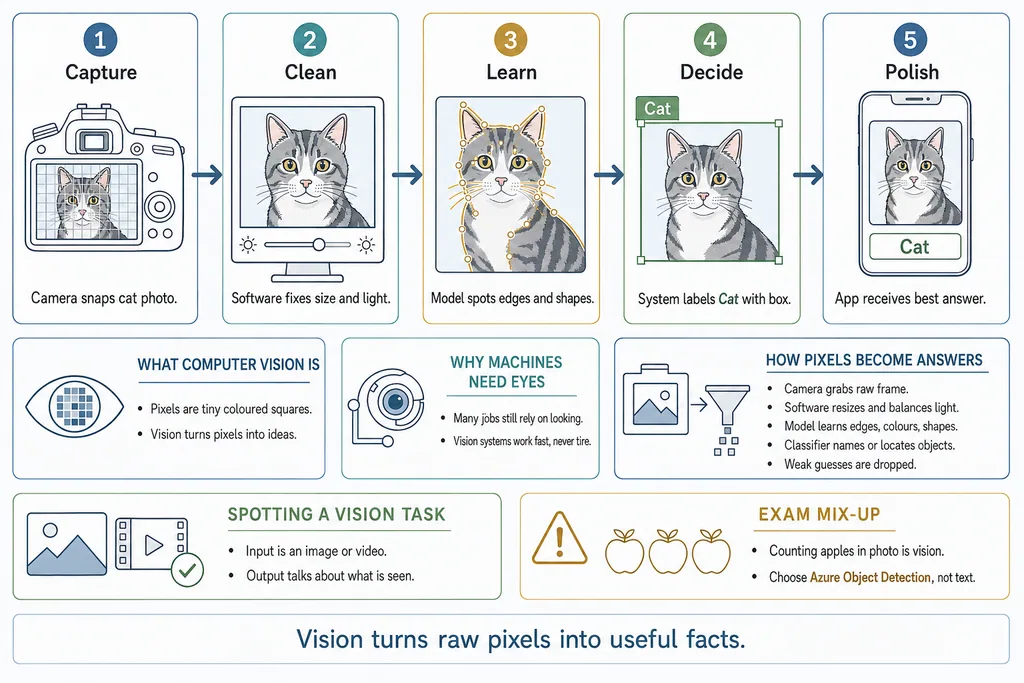
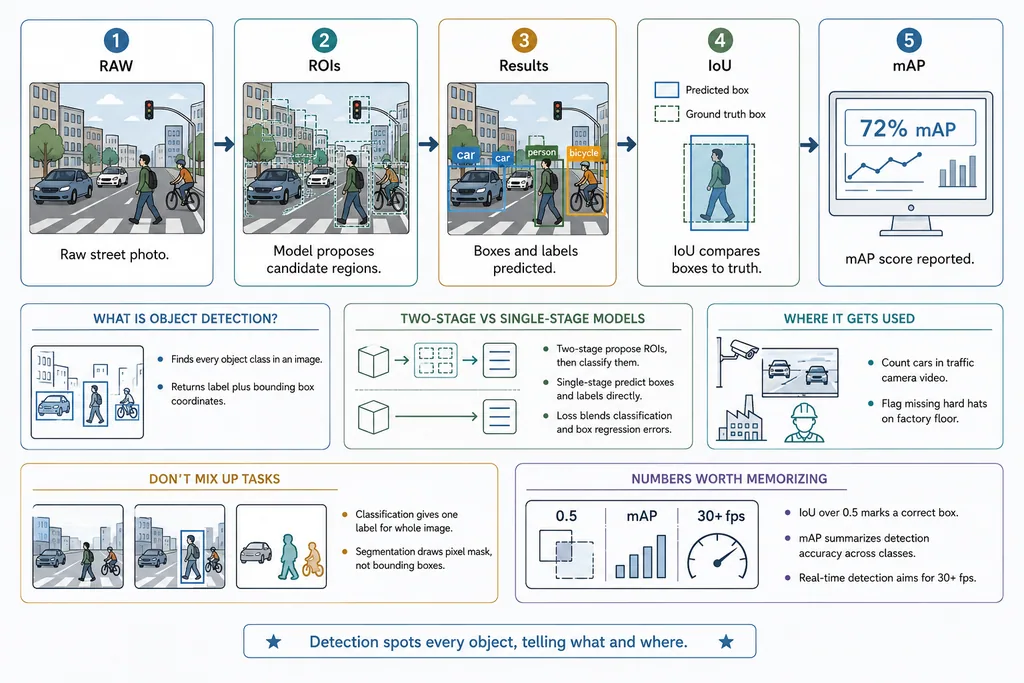
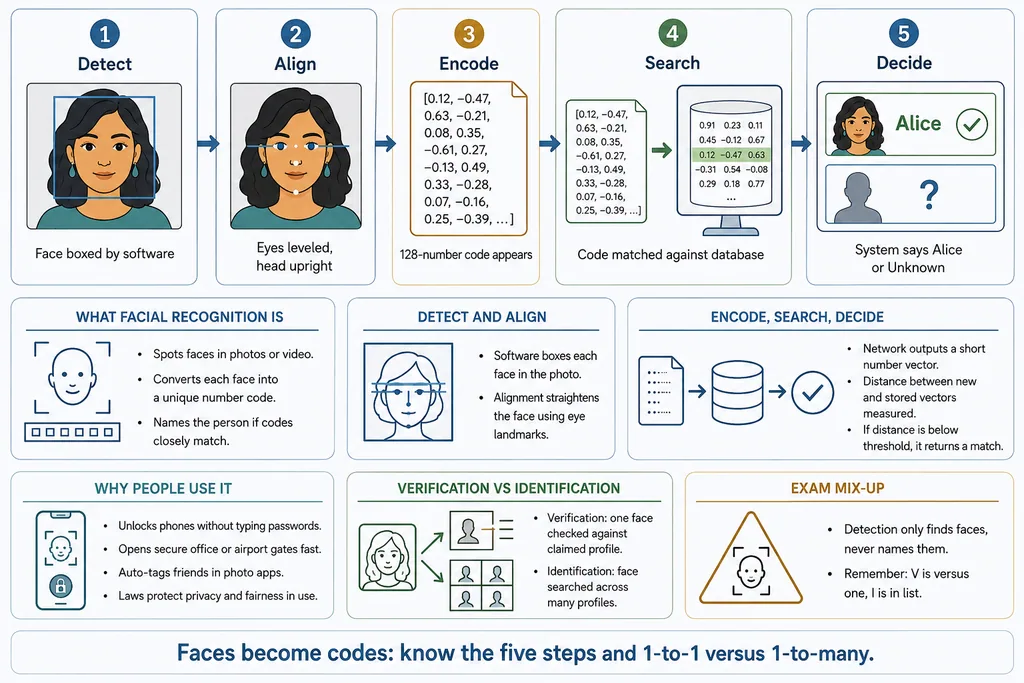
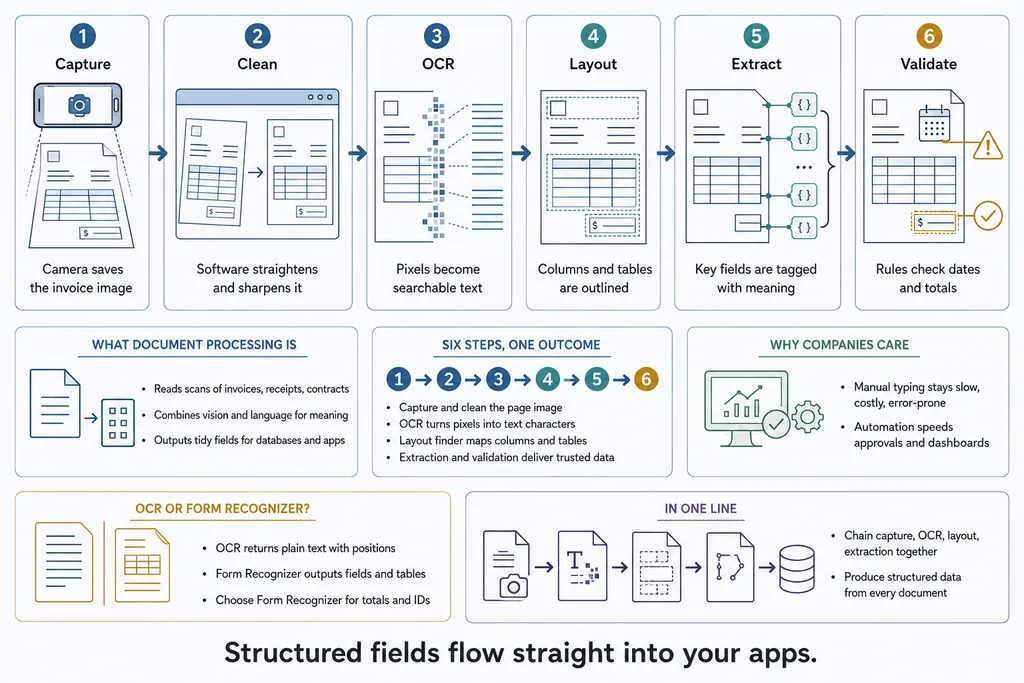
Every objective below is a page you can open and practise now, without an account.
The official F5 exam outline · checked 30 July 2026 · See the source
In front of every objective the practice pages are already there, free and without an account. This is one objective, opened.
21 questions on this objective, five to a page. Every range above is a real page, open now, with no account.
The curriculum tells you what is on the exam. Proving you know it is a different job — and it is the one the closed-book run does.
The whole bank is open. 5 questions to a page, every answer explained, and a discussion thread on each one.
Every objective, and every page range, is a link — so you can pick up exactly where you left off.
Short enough to finish, long enough to matter.
Not only which one is right — why the others are wrong.
Ask, answer, and vote. Every question has its own thread.
These are not trivia. Each one is written against a concept in the book, so when you get one wrong there is somewhere to go and find out why.
The pages shown here come from our AI-900 book — an example of how each concept is written in plain language and, where the idea needs one, drawn as a full page you can take in at a glance.
Three reasons, and each one is a real finding rather than a slogan.
You can see it againUnder pressure people bring back shapes and positions long after the wording has gone.
Picture superiority · Shepard 1967, Standing 1973The whole idea at onceWhere it starts, what happens in the middle, what comes out, and the mistake to avoid.
Multimedia principle · MayerThe look-alikes sit togetherThe pairs the exam tests are drawn side by side, so the difference is seen, not told.
Dual coding · PaivioYou are never asked to read a poster here — only to see how one is built. After that, every other page is legible at a glance.
The idea as a sequence, followed with a finger before a word is read.
What it is, how the machine learns it, when it is the right tool.
The distinction the exam tests, given its own box instead of buried in prose.
The sentence to carry into the exam room.
This is the part that teaches. The illustration and the written explanation stay where they are while you work, so a scenario stops being a memory test and becomes something you can simply look at.
A smartphone uses AI to unlock when the owner looks at the camera. Which AI capability is being used?
The same questions come back with the book closed — that run is the one that counts. After it, your coach picks one thing for tonight, sized to the time you have, and brings pages back before you lose them.
Testing effect · Roediger & Karpicke 2006 · spacing effect · Cepeda et al. 2006
Straight from F5Where the exam is defined, scheduled and scored.
We link to them rather than repeat them, so nothing here goes stale behind them.
We build from the official skills outline, not from a summary of it — 42 objectives, 224 concepts written under them, and free questions against every one. When F5 changes the outline, this page changes with it.
That is the only question worth answering the night before, and no link answers it. You answer it by taking the questions with the book closed, and seeing what comes back.