 You can see it again
Under pressure people bring back shapes and positions long after the wording has gone.
Picture superiority · Shepard 1967, Standing 1973 Examers.io

 SPLUNK
The Splunk Enterprise Certified Admin certification validates your ability to manage and maintain the day-to-day health of a Splunk Enterprise environment. You'll demonstrate expertise in license management, indexers, search heads, configuration, monitoring, and data ingest. This credential is ideal for administrators who support Splunk Enterprise deployments and want to advance their careers beyond searches and dashboards.
Content last reviewed 30 July 2026 · Up to date
What this certification covers, who it is written for, and what the exam itself looks like on the day.
What it validates, who it is written for, and the experience it assumes.
The Splunk Enterprise Certified Admin certification validates your ability to manage and maintain the day-to-day health of a Splunk Enterprise environment. You'll demonstrate expertise in license management, indexers, search heads, configuration, monitoring, and data ingest. This credential is ideal for administrators who support Splunk Enterprise deployments and want to advance their careers beyond searches and dashboards.
Earning this certification shows you have the skills to optimize the health of your Splunk Enterprise environment, from managing licenses and configuring data inputs to troubleshooting issues and ensuring smooth operations. It's a key stepping stone for those looking to administer Splunk Enterprise Security environments or pursue the Splunk Enterprise Certified Architect certification.
This certification is for anyone responsible for supporting the day-to-day administration and health of a Splunk Enterprise environment. It's ideal for platform administrators who manage and maintain their Splunk Enterprise environment's health, and for those who want to grow their career beyond searches and dashboards within the Splunk Enterprise platform. It's also a valuable credential for Enterprise Security administrators looking to enhance their credentials and expertise, serving as a key stepping stone to successfully administering a Splunk Enterprise Security environment.
Splunk recommends that candidates have experience as a Splunk Core Certified Power User and are familiar with the day-to-day administration of a Splunk Enterprise environment. Experience managing Splunk Enterprise on a daily basis; Knowledge of license management, indexers, and search heads; Understanding of configuration, monitoring, and data ingest; Familiarity with Splunk Core Certified Power User skills
Every domain and objective Splunk measures, with the weight they carry on the exam.
The official Splunk exam outline · checked 30 July 2026 · See the source
Everything Splunk publishes about sitting it, and nothing we inferred.
Splunk Core Certified Power User
The path Splunk lays out, how the credential is kept, and where to book.
Step-by-step path to Splunk Enterprise Certified Admin
Credential earnedSplunk Enterprise Certified Admin CertificationSplunk certifications must be renewed every three years. You can renew by pursuing additional certifications, completing continuing education courses, or re-taking your certification exam. Stay current with the latest technologies and maintain your certification.
Learn more about renewal requirementsThis certification is currently active and available. Splunk maintains this certification to validate current skills and industry relevance.
Register for the exam through Pearson VUE, Splunk’s authorized testing partner.
Schedule your examVisit the official Splunk certification page for exam policies and requirements.
View the official pageYour coach in the app reads what you have answered with the book closed and tells you one thing to do tonight. It will not count an answer you gave with the page open, and it will tell you when you are not ready.
See how the coach worksThe Splunk Enterprise Certified Admin exam focuses on managing on-premises Splunk Enterprise environments, while the Splunk Cloud Certified Admin exam covers administering Splunk Cloud. They are separate certifications with different exam codes and prerequisites.
Yes, the Splunk Core Certified Power User certification is a mandatory prerequisite for the Splunk Enterprise Certified Admin exam.
No, the SPLK-1003 exam consists of 56 multiple-choice questions only. There is no hands-on lab or performance-based component.
Splunk's retake policy requires a waiting period of 24 hours after a first failed attempt, and 14 days before each subsequent attempt. There is no annual cap on attempts.
This credential is designed for Splunk Enterprise administrators, platform administrators, and IT professionals responsible for the day-to-day administration and health of a Splunk Enterprise environment.
Yes, earning a higher-level Splunk certification, such as the Splunk Enterprise Certified Architect, can renew your Splunk Enterprise Certified Admin certification.
Every domain, every objective, and every concept Splunk measures — each one written out.
Every objective below is a page you can open and practise now, without an account.
The official Splunk exam outline · checked 30 July 2026 · See the source
In front of every objective the practice pages are already there, free and without an account. This is one objective, opened.
18 questions on this objective, five to a page. Every range above is a real page, open now, with no account.
The curriculum tells you what is on the exam. Proving you know it is a different job — and it is the one the closed-book run does.
The whole bank is open. 5 questions to a page, every answer explained, and a discussion thread on each one.
Every objective, and every page range, is a link — so you can pick up exactly where you left off.
Short enough to finish, long enough to matter.
Not only which one is right — why the others are wrong.
Ask, answer, and vote. Every question has its own thread.
These are not trivia. Each one is written against a concept in the book, so when you get one wrong there is somewhere to go and find out why.
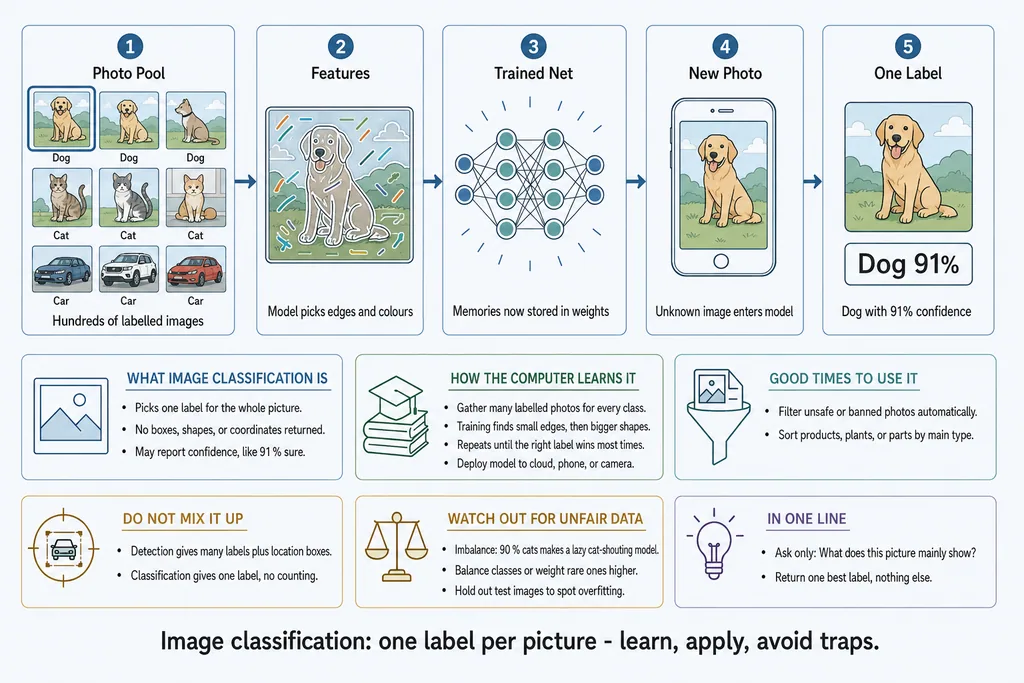
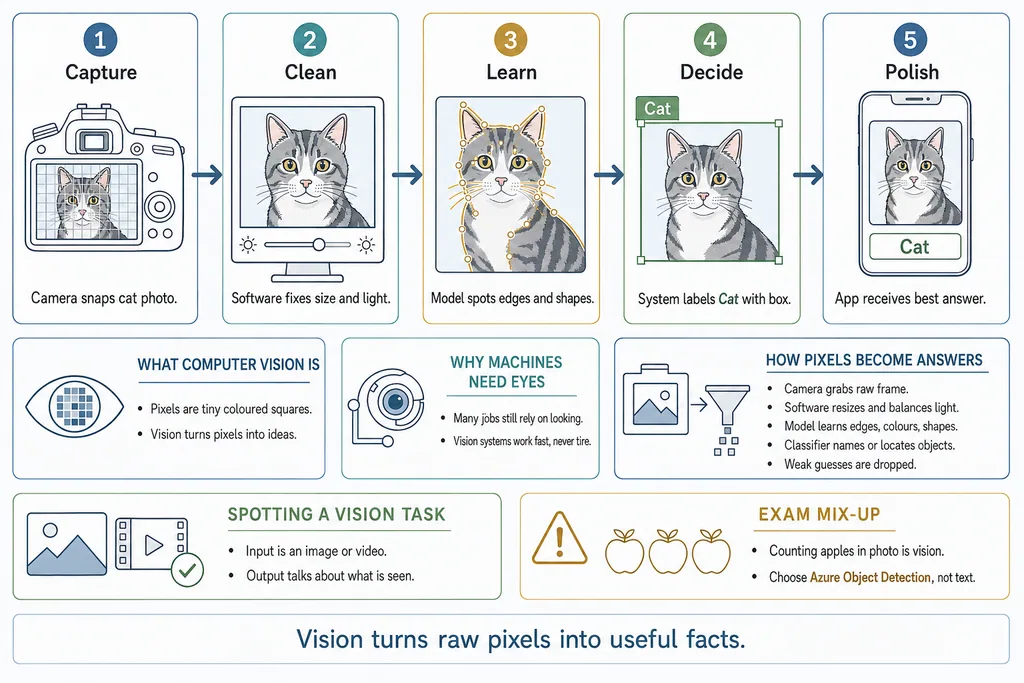
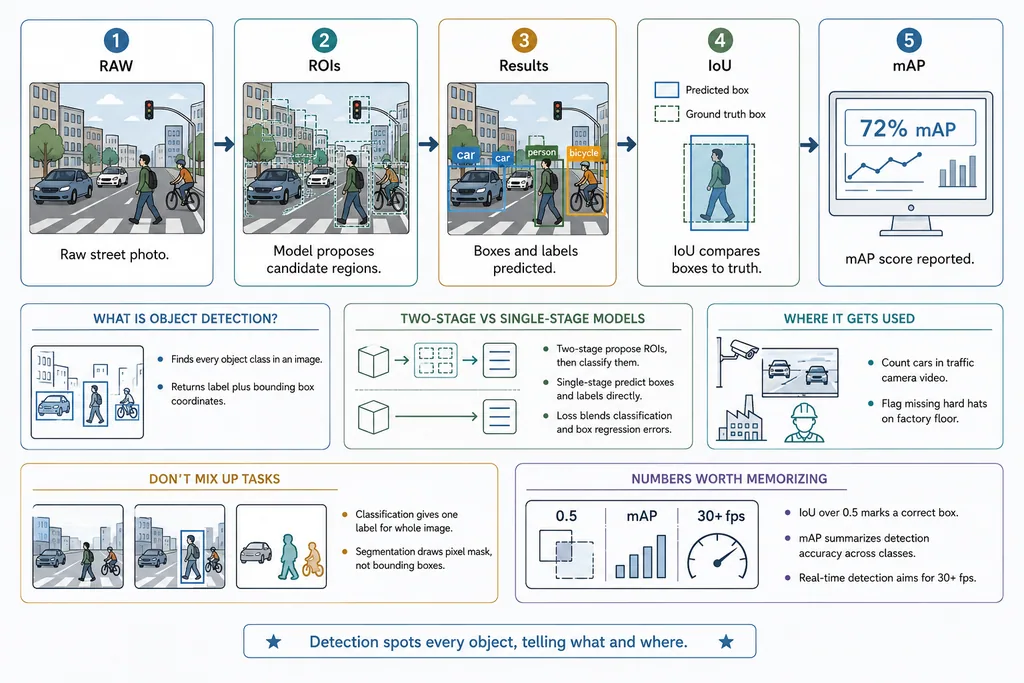
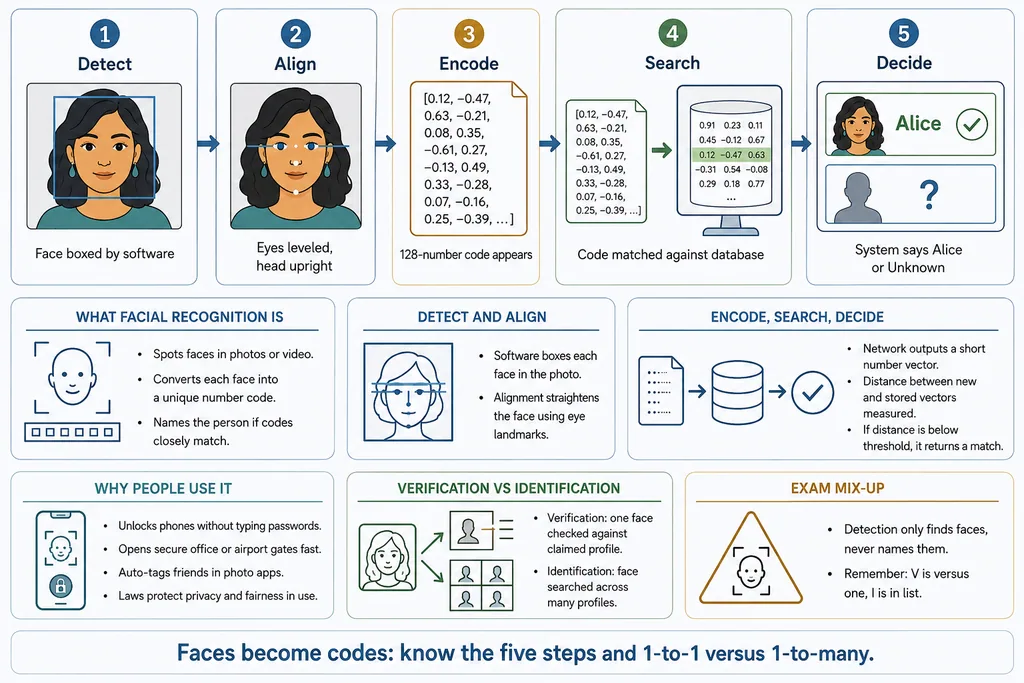
The pages shown here come from our AI-900 book — an example of how each concept is written in plain language and, where the idea needs one, drawn as a full page you can take in at a glance.
Three reasons, and each one is a real finding rather than a slogan.
You can see it againUnder pressure people bring back shapes and positions long after the wording has gone.
Picture superiority · Shepard 1967, Standing 1973The whole idea at onceWhere it starts, what happens in the middle, what comes out, and the mistake to avoid.
Multimedia principle · MayerThe look-alikes sit togetherThe pairs the exam tests are drawn side by side, so the difference is seen, not told.
Dual coding · PaivioYou are never asked to read a poster here — only to see how one is built. After that, every other page is legible at a glance.
The idea as a sequence, followed with a finger before a word is read.
What it is, how the machine learns it, when it is the right tool.
The distinction the exam tests, given its own box instead of buried in prose.
The sentence to carry into the exam room.
This is the part that teaches. The illustration and the written explanation stay where they are while you work, so a scenario stops being a memory test and becomes something you can simply look at.
A smartphone uses AI to unlock when the owner looks at the camera. Which AI capability is being used?
The same questions come back with the book closed — that run is the one that counts. After it, your coach picks one thing for tonight, sized to the time you have, and brings pages back before you lose them.
Testing effect · Roediger & Karpicke 2006 · spacing effect · Cepeda et al. 2006
Straight from SplunkWhere the exam is defined, scheduled and scored.
We link to them rather than repeat them, so nothing here goes stale behind them.
We build from the official skills outline, not from a summary of it — 24 objectives, 135 concepts written under them, and free questions against every one. When Splunk changes the outline, this page changes with it.
That is the only question worth answering the night before, and no link answers it. You answer it by taking the questions with the book closed, and seeing what comes back.